TOOLNAVIA / BUYING GUIDE
MailerLite Domain Authentication: Fix SPF, DKIM and DMARC Before Upgrading
The short answer
MailerLite can ask you to authenticate a custom sending domain with DKIM, SPF and a verification record. If that screen appears near the end of a trial, it is easy to assume the remedy is a paid plan. The official material reviewed for this guide does not establish that authentication itself is a paid-only entitlement.
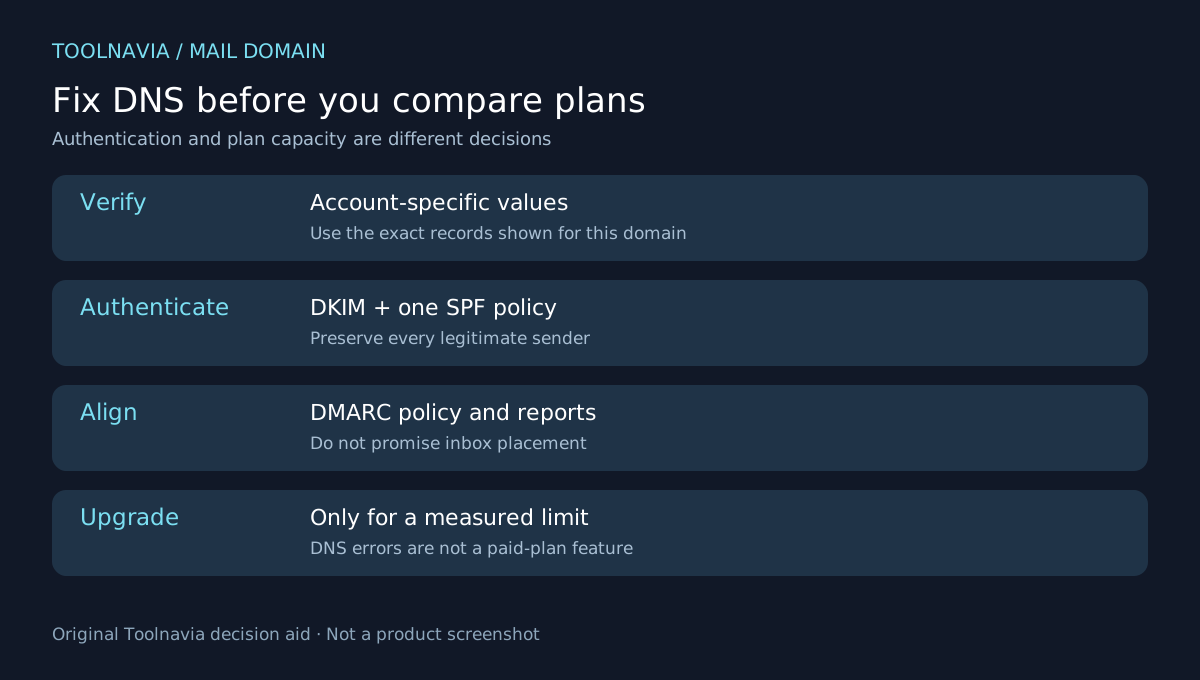
The safer buying decision is to fix and verify DNS first. Upgrade only when a separately documented limit—subscriber count, monthly sends, users, automation capacity, websites or forms—actually blocks the workflow.
*Official documentation was reviewed on October 30, 2026. No live MailerLite Free account, DNS zone, campaign or inbox-placement test was performed. Post-trial Free availability is an evidence-based inference, not a verified plan-row promise.*
At a glance
- Best for
- Teams that control sending-domain DNS and want to authenticate safely before buying more capacity.
- Price model
- No numeric price conclusion; verify selected checkout, renewal, tax and market after authentication passes.
- Check first
- No Free entitlement, inbox placement or live DNS test is promised; account-specific records and checkout control.
Separate three different questions
A domain-authentication warning can hide three independent decisions:
1. **Can MailerLite verify that you control the domain?** This uses the verification value shown in the account. 2. **Can recipients validate MailerLite as an authorized sender?** DKIM signs the message; SPF identifies permitted sending infrastructure. 3. **What should receivers do when alignment fails?** DMARC publishes policy and reporting instructions.
None of those questions is identical to “Which MailerLite plan should I buy?” MailerLite’s trial help says a custom-domain sender must authenticate after the trial to continue sending, while the account otherwise reverts to the Free plan. That supports—but does not explicitly prove—the inference that authentication remains possible without Comfort.
Do not publish “Comfort unlocks SPF/DKIM” unless a current official plan row or a real account test proves it.
Inventory every sender before touching SPF
The most dangerous shortcut is deleting an existing SPF record because a provider-specific setup page says to replace it. A domain can already authorize Google Workspace, Microsoft 365, a support desk, a transaction provider or another marketing platform.
Before changing DNS:
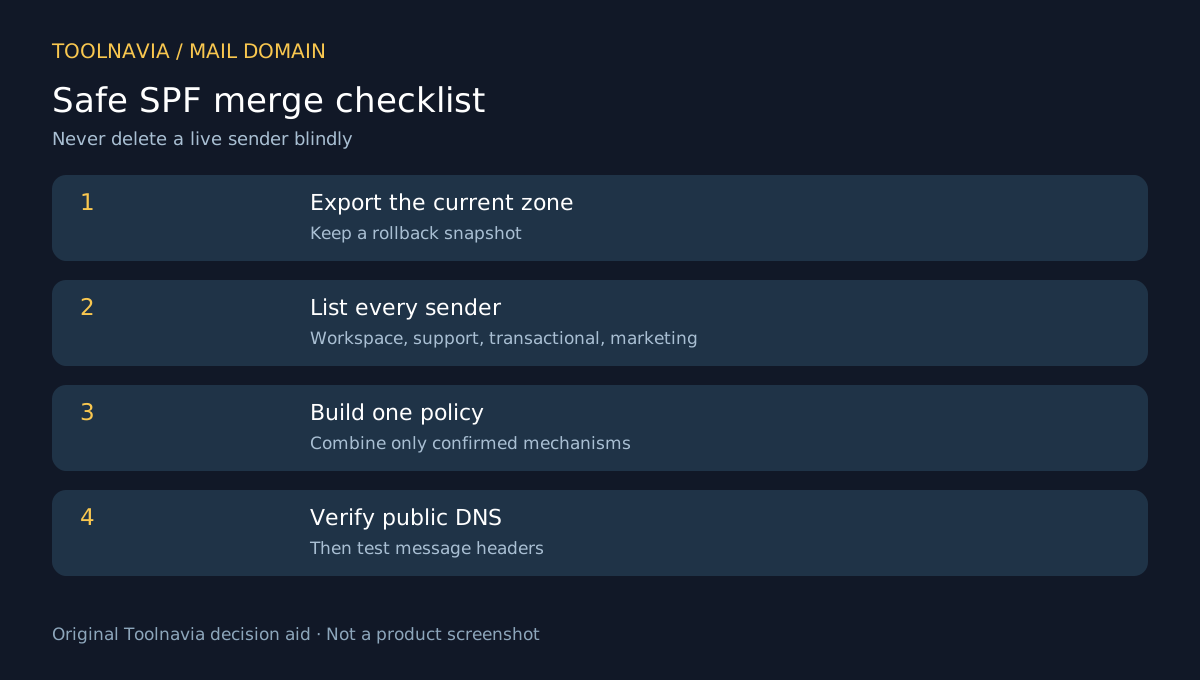
- export or copy the current zone; - list every system that sends mail using the domain; - record the existing SPF TXT value; - identify who owns the registrar or DNS provider account; - choose a rollback point and maintenance window.
A domain should normally have one SPF policy record. If several legitimate services must send, combine their authorized mechanisms into one valid policy rather than publishing competing SPF records. MailerLite’s troubleshooting guide explicitly warns about multiple SPF records and allows DNS propagation time.
This is not a universal instruction to append every old value. Remove an obsolete sender only after its owner confirms it is no longer used.
Add the MailerLite records exactly as shown
Use the values displayed inside the MailerLite account for the exact sending domain. Do not copy selectors, hosts or verification tokens from an article or another account.
A controlled setup sequence is:
1. Open MailerLite’s domain-authentication screen and capture the required DKIM CNAME, SPF TXT and verification TXT values. 2. In the DNS provider, confirm whether the interface automatically appends the zone name. Entering the full host twice can create a wrong record. 3. Preserve existing authorized senders while constructing the single SPF policy. 4. Add the DKIM selector and target exactly as issued. 5. Add the verification record separately; it is not a substitute for SPF or DKIM. 6. Save a before-and-after snapshot with the time and operator. 7. Wait for propagation, then rerun MailerLite’s verification.
Do not expose verification tokens in public screenshots. If DNS is managed by an agency or IT team, send them the values through an approved private channel.
Treat DKIM, SPF and DMARC as different evidence
A green result for one record does not prove the whole chain works.
- **DKIM**: confirm the selector resolves to the target issued by MailerLite. A selector copied from another domain or account is not evidence. - **SPF**: confirm there is one coherent policy and that every current sender remains authorized. - **DMARC**: confirm the policy domain and reporting addresses are controlled and aligned with the actual From domain. - **Message evidence**: after DNS verification, send an authorized test campaign and inspect the authentication results in the message headers.
MailerLite describes DMARC as a separate policy and reporting layer. It does not guarantee inbox placement. Reputation, content, recipient engagement, complaint history and list hygiene still matter.
Start DMARC enforcement only when the organization has reviewed its full sending inventory. An aggressive reject policy can block legitimate but unaligned systems.
Diagnose failures without buying first
When MailerLite still reports a failure, check the narrowest observable cause:
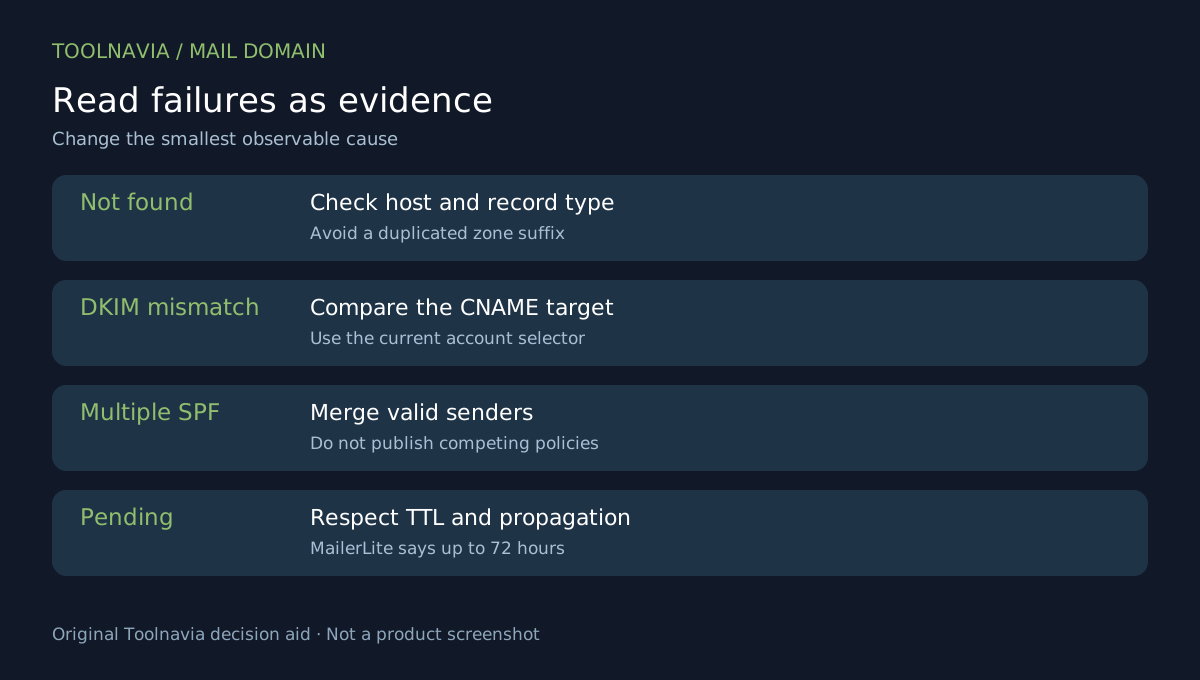
- **Record not found**: inspect the public DNS answer for the exact host and record type. - **Wrong DKIM target**: compare the live CNAME target character by character with the account value. - **Multiple SPF records**: merge legitimate mechanisms into one policy and remove only confirmed duplicates. - **Propagation delay**: note the DNS provider’s TTL and wait for caches; MailerLite says propagation can take up to 72 hours. - **Proxy or flattening behavior**: confirm the DNS provider is not altering a record that must remain a CNAME. - **Domain mismatch**: verify the authenticated domain matches the visible From domain used by the campaign.
Changing plans does not repair a mistyped host, a duplicated zone suffix or an invalid SPF policy. If the DNS result is correct but MailerLite still fails, preserve screenshots and public lookup evidence before contacting support.
Compare competitors for the right lesson
Mailchimp, Kit and Brevo also document domain verification and authentication as DNS trust work rather than a simple upgrade cure. Their exact records and entitlement rules are not transferable to MailerLite, but their guidance reinforces three neutral principles:
- verification and authentication are separate; - DNS values must come from the active account; - authentication improves trust signals but does not promise delivery.
Do not add a competitor’s DKIM selector, SPF include or DMARC policy to a MailerLite setup.
Twilio SendGrid likewise treats domain authentication as provider-specific DNS configuration; its values cannot be copied into MailerLite.
Decide whether Comfort solves a different bottleneck
After authentication passes, map the remaining limit to the current MailerLite pricing table. Consider Comfort only when the selected plan changes a measured need, such as subscriber capacity, send allowance, seats or another explicitly listed feature.
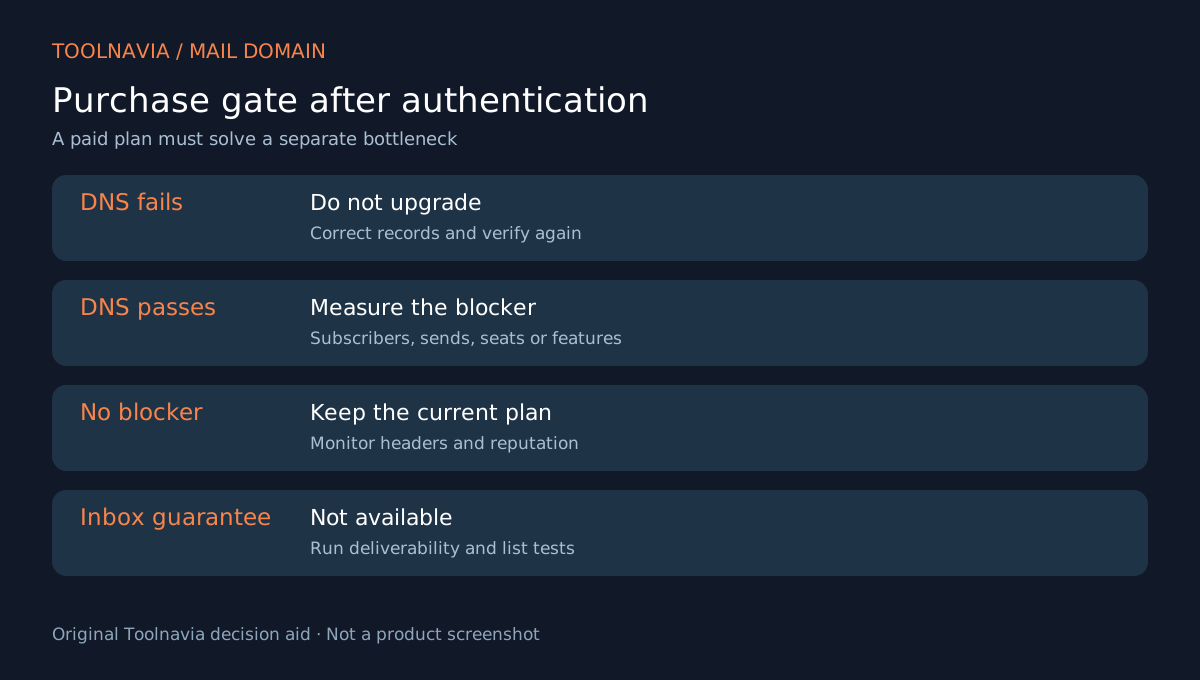
Use this purchase gate:
- **DNS still failing** → fix DNS; do not upgrade for authentication. - **DNS passes, plan limit blocks work** → compare the exact plan row and selected checkout. - **DNS passes, no documented limit blocks work** → keep the current plan and monitor. - **Need guaranteed inbox placement** → no plan can promise it; run deliverability and list-quality tests.
Prices, taxes, billing intervals and feature labels can change. Confirm the selected market and checkout immediately before paying. No price is quoted here because this article’s decision is authentication versus capacity, not a dated price snapshot.
Keep an evidence packet
For every production sending domain, retain:
- the approved sender inventory; - the DNS before/after snapshots; - the exact MailerLite values and verification time; - a test-message header showing SPF, DKIM and DMARC results; - the person who approved enforcement changes; - the rollback plan.
Repeat the check after changing DNS providers, From domains or mail platforms. A record that passed last year does not prove today’s route is aligned.
Verdict
Do not buy MailerLite Comfort merely because domain authentication is incomplete. The available official evidence does not show authentication as a paid-only switch, and the post-trial Free-plan conclusion remains an inference until verified in an explicit plan row or real Free account.
Authenticate the sending domain carefully, preserve other legitimate senders, validate headers, and upgrade only for a separately evidenced capacity or workflow limit.
*Affiliate disclosure: Toolnavia may earn a commission if you later choose MailerLite through an approved link. No exclusive discount, DNS repair, inbox placement or Free-plan entitlement is promised.*